A mid-sized logistics company in Jurong found out the hard way what it means to operate infrastructure the state considers critical. After a ransomware attempt disrupted part of its warehouse management system, the company assumed the incident was purely an internal IT matter to be handled quietly and resolved without outside involvement. It was not.
Because the firm’s systems connected into port logistics networks classified as critical information infrastructure, the incident triggered mandatory reporting obligations the company’s management had never fully registered as applying to them. The episode is a useful illustration of how Singapore’s cybersecurity regime reaches well beyond banks and telecom operators into ordinary businesses whose systems happen to sit inside a wider critical network.
Singapore’s Cybersecurity Act Explained
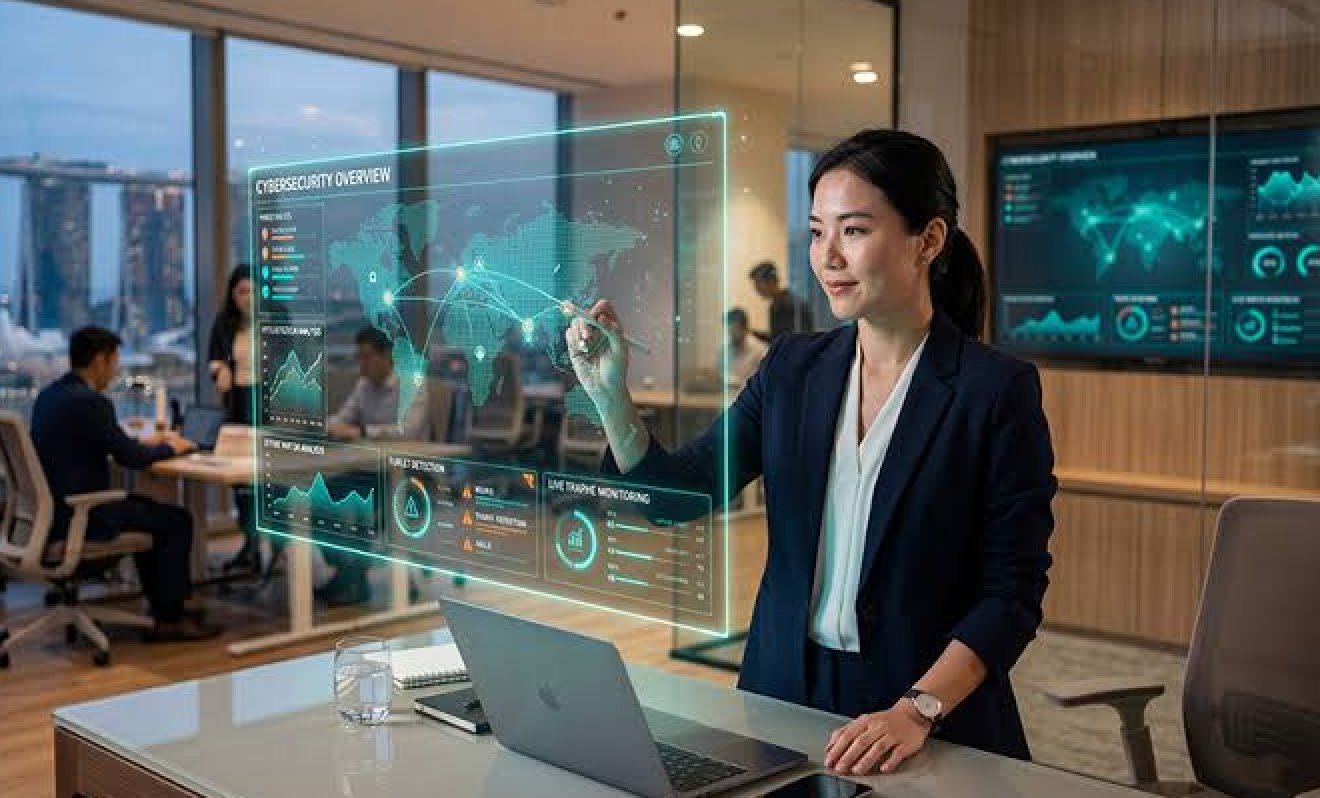
The Cybersecurity Act establishes the legal backbone for how the state identifies, monitors, and responds to cyber threats affecting essential services. Administered by the Cyber Security Agency of Singapore, commonly referred to as CSA, the Act gives the agency powers to designate specific systems as critical information infrastructure, investigate cybersecurity incidents, and set binding codes of practice that owners of designated systems must follow.
The framework rests on a layered logic. Rather than regulating every computer system in the economy uniformly, it concentrates the heaviest obligations on systems whose disruption would have outsized consequences for essential services such as energy, water, healthcare, banking, and transport. Businesses outside these designated categories still operate under general data protection and contractual obligations, but the Act’s most demanding requirements are reserved for infrastructure the state has formally identified as critical.
This layered structure also reflects a practical constraint any regulator faces: resources for close, continuous supervision are finite, and spreading them evenly across every business in the economy would dilute oversight precisely where the consequences of failure are most severe. By concentrating scrutiny on designated systems, CSA can maintain a depth of engagement frequent audits, direct incident coordination, sector-specific codes of practice that would simply not be sustainable if applied uniformly to every company handling any form of digital data. Businesses sitting just outside the critical infrastructure boundary sometimes view this as a lighter compliance burden, though in practice they still answer to a wider set of overlapping obligations under contract law, sector licensing conditions, and general data protection legislation.
Critical Information Infrastructure Obligations
Once a system is designated as critical information infrastructure, its owner takes on a distinct set of legal duties that go well beyond ordinary IT best practice. These obligations are not voluntary guidelines they carry the force of law, with CSA empowered to issue directions and, where necessary, penalties for non-compliance.
Designated owners typically must:
- Conduct regular audits: independent cybersecurity audits at defined intervals to verify that controls match the code of practice CSA has issued for that sector.
- Perform risk assessments: periodic evaluation of vulnerabilities specific to the designated system, updated as the technology environment changes.
- Report incidents promptly: notify CSA of cybersecurity incidents affecting the critical system within a defined timeframe, even before the full scope of the incident is known.
- Participate in exercises: take part in cybersecurity readiness exercises coordinated by CSA to test incident response across sectors.
- Maintain documentation: keep records demonstrating compliance available for inspection, since CSA can request evidence at any point, not only after an incident.
Sector-Specific Requirements for Businesses
Beyond critical information infrastructure, Singapore’s regulatory landscape layers sector-specific cybersecurity expectations on top of the general framework. Financial institutions answer to additional technology risk management guidelines from MAS, which set detailed expectations around system resilience, third-party technology risk, and incident notification timeframes distinct from those under the Cybersecurity Act itself. Healthcare providers face their own expectations tied to the sensitivity of medical data, while telecommunications operators are subject to licence conditions that fold in cybersecurity resilience requirements directly.
These sector-specific guidelines tend to be updated more frequently than the broader Cybersecurity Act framework, reflecting the pace at which technology risk itself evolves within fast-moving industries such as banking. Compliance teams within banks and insurers often describe keeping pace with these updates as one of the more resource-intensive parts of their regulatory obligations, precisely because the expectations are detailed and specific rather than expressed as broad principles open to wide interpretation. Businesses operating across more than one regulated sector should map out a few things early:
- Overlapping obligations: which systems fall under more than one regime simultaneously, such as a bank’s critical payment infrastructure.
- Differing reporting timeframes: sector guidelines and the Cybersecurity Act do not always share identical incident notification windows.
- Primary supervisory contact: which regulator takes the lead where obligations overlap, to avoid duplicated or conflicting reporting.
This layering is a direct consequence of Singapore’s broader regulatory style, which tends to build sector-specific rules on top of general legislation rather than folding every requirement into one master statute. This layering means a single business can find itself answering to more than one regulatory regime simultaneously a bank, for example, sits under both MAS technology risk expectations and, if any of its systems are designated as critical information infrastructure, the Cybersecurity Act as well. Businesses operating across sectors need to map which regime applies to which system rather than assuming a single compliance programme covers everything by default.
Conglomerates spanning several regulated sectors face this challenge most acutely. A group with a banking arm, a healthcare subsidiary, and a logistics division may need three distinct compliance programmes running in parallel, each calibrated to a different regulator’s expectations, reporting timeframes, and audit cadence, even though a single group-level cybersecurity function often coordinates the underlying technical controls. Building this kind of layered compliance structure benefits from early legal mapping exercises that clarify precisely which entity within a group answers to which regulator for which system, rather than leaving that determination until a regulator’s inquiry forces the question.
Incident Reporting Duties
Reporting obligations form one of the most operationally demanding parts of the regime, precisely because incidents rarely announce themselves with full clarity at the outset. A designated critical information infrastructure owner must notify CSA of an incident within a defined window from when it is discovered, well before a full forensic investigation could reasonably be completed. This forces businesses to build reporting processes that can move on incomplete information, escalating as more detail emerges rather than waiting for a tidy, final assessment.
Practical incident response therefore depends on internal readiness as much as external reporting rules. Businesses that have not rehearsed an incident response plan tend to lose critical hours simply deciding who has authority to report, what needs to be included in an initial notification, and how to communicate with customers or partners without compounding the damage. Tabletop exercises, where a management team walks through a simulated incident scenario without any real system being affected, remain one of the more effective ways to surface exactly these gaps before a real incident forces the answers to be worked out under pressure. A mature incident response plan typically distinguishes between:
- Initial notification: a fast, necessarily incomplete report flagging that an incident has occurred and is under investigation.
- Follow-up reporting: subsequent updates as the scope, cause, and impact become clearer.
- Closure reporting: a final account once remediation is complete, often including lessons learned that feed back into future risk assessments.
Penalties for Non-Compliance
The Cybersecurity Act gives CSA a graduated set of enforcement tools, ranging from directions requiring a business to remediate specific weaknesses, to financial penalties for failing to comply with reporting or audit obligations. For designated critical information infrastructure owners, non-compliance is treated seriously because the consequences of a successful attack on such systems extend beyond the individual company to essential services relied upon by the wider public.
Penalties are not the only consequence businesses should weigh, however. A publicised cybersecurity failure whether or not it triggers formal enforcement action carries reputational costs that can outlast any fine imposed by a regulator, notably for businesses whose customers or partners depend on trust in the confidentiality and availability of shared systems. This dynamic pushes many businesses to treat regulatory minimums as a floor rather than a target, investing in resilience that exceeds strict legal requirements.
Insurance has become a further layer businesses weigh alongside direct regulatory penalties. Cyber insurance policies increasingly require evidence of baseline controls patching discipline, access management, backup practices before offering coverage, and a business found to have misrepresented its security posture to an insurer can find a claim denied precisely when it is needed most. This has created an indirect but powerful incentive for businesses to document their cybersecurity practices accurately, since the documentation supporting a regulatory compliance programme often doubles as the evidence an insurer requires during underwriting or after a claim is filed.
Building a Compliance Roadmap
Businesses approaching cybersecurity compliance for the first time often struggle less with grasping individual rules than with sequencing the work sensibly. A practical roadmap generally starts with an honest inventory of systems and data, followed by a gap assessment against the relevant regulatory code of practice, and only then moves into remediation and process design.
A workable sequence typically includes:
- System inventory and classification: mapping which systems handle sensitive data or connect to critical infrastructure, since obligations scale with this classification.
- Gap assessment: comparing current controls against the applicable regulatory baseline to identify the most urgent deficiencies.
- Remediation prioritisation: addressing the highest-risk gaps first rather than pursuing every improvement simultaneously, which is rarely realistic for a resource-constrained business.
- Governance assignment: naming clear internal ownership for cybersecurity compliance, since diffuse responsibility is one of the most common causes of missed reporting deadlines.
- Ongoing monitoring: establishing a cadence of review rather than treating compliance as a one-time project.
Businesses that build this roadmap as a one-off project, rather than an ongoing operational cadence, often find that compliance quietly erodes over time as systems change, new vendors are onboarded, or staff turnover leaves gaps in institutional knowledge about why a particular control exists. Treating the roadmap as a living document, revisited on a fixed schedule rather than only when a regulator or auditor asks for an update, tends to produce a compliance posture that holds up better under real scrutiny.
Third-Party Vendor Risk Management
A growing share of cybersecurity exposure for Singapore businesses now originates not from their own systems but from vendors and service providers they depend on. Cloud hosting providers, payment processors, and outsourced IT support all introduce risk that a business cannot fully control through its own internal measures alone. Regulators have responded by pushing accountability upstream a business cannot simply point to a vendor’s failure as an excuse for its own compliance gaps.
Effective vendor risk management generally involves contractual clauses requiring vendors to meet specified security standards, periodic assessment of vendor practices rather than a one-time onboarding check, and contingency planning for scenarios where a key vendor suffers its own incident. Businesses that rely heavily on a small number of critical vendors face particular exposure here, since a single vendor failure can cascade across multiple downstream businesses simultaneously.
Contract negotiations increasingly reflect this heightened awareness, with businesses pushing for specific service level commitments around security incident notification timeframes from vendors, mirroring the reporting obligations the business itself faces under regulation. A vendor unwilling to accept reasonable security obligations in a contract is itself a signal worth weighing carefully before finalising a relationship involving sensitive systems or data.
Businesses often underestimate how many layers deep this exposure runs. A payment processor’s own reliance on a cloud infrastructure provider, which in turn relies on specialised network hardware suppliers, means a business assessing “vendor risk” narrowly at the first tier can still be blindsided by a failure two or three tiers removed from any relationship it directly manages. Larger organisations have begun asking key vendors to disclose their own critical dependencies as part of onboarding, extending the visibility of vendor risk management beyond the immediate contractual relationship into the broader supply chain that ultimately supports it.
Final Thoughts
Cybersecurity regulation in Singapore has moved from a narrow concern for a handful of large infrastructure operators to a layered system touching a much broader range of businesses, often in ways companies do not fully register until an incident forces the issue.
The framework’s core logic concentrate the heaviest obligations where disruption would matter most, while still expecting baseline diligence everywhere else gives businesses a reasonably predictable structure to build compliance around, provided they take the time to map which regime specifically applies to their systems. Treating cybersecurity as an operational discipline rather than a document to file away tends to separate businesses that recover quickly from incidents from those that do not.
Frequently Asked Questions
1. How does a business know if its systems qualify as critical information infrastructure?
CSA formally designates specific systems as critical information infrastructure based on their role in delivering essential services, and owners are notified directly of this designation rather than needing to self-identify from general criteria. Businesses providing services in sectors such as energy, water, healthcare, banking, or transport should proactively engage with CSA if they suspect their systems might qualify, rather than waiting for designation to be confirmed only after an incident forces the question into the open. Designation brings specific legal obligations that begin from the date of formal notice.
2. Do small businesses without critical infrastructure have any cybersecurity obligations?
Yes, though the obligations differ in nature from those applying to designated critical infrastructure. General data protection law still requires reasonable security arrangements to protect personal data, and contractual obligations with larger partners often impose additional cybersecurity expectations regardless of formal CSA designation. Smaller businesses should not assume that falling outside the Cybersecurity Act’s strictest provisions means cybersecurity carries no legal weight for them at all.
3. What is the difference between CSA’s role and MAS’s technology risk requirements?
CSA administers the Cybersecurity Act broadly across sectors and focuses on critical information infrastructure resilience at a national level, while MAS sets technology risk management expectations specifically for financial institutions, covering areas such as system availability, outsourcing risk, and incident notification within the financial sector. A financial institution with designated critical infrastructure can be subject to both regimes concurrently, each with its own specific requirements and reporting timeframes.
4. How quickly must a cybersecurity incident be reported?
Reporting timeframes are defined by regulation and vary depending on the sector and the nature of the incident, but the general expectation across regimes is that notification happens promptly after discovery rather than after a full investigation concludes. Businesses are expected to file an initial report with the information available and follow up as more facts emerge. Waiting for complete certainty before reporting is treated as a compliance failure in itself.
5. Can a business be penalised for an incident caused entirely by a third-party vendor?
Potentially, yes, notably where the business failed to exercise reasonable oversight of that vendor’s security practices or contractual obligations. Regulators generally expect the business holding the primary relationship with customers or critical services to maintain accountability for the overall security posture, including risks introduced through outsourcing. This is a key reason vendor due diligence has become a standard part of cybersecurity compliance programmes.
6. What role do cybersecurity exercises play in the regulatory framework?
CSA coordinates sector-wide exercises designed to test how businesses, notably those with critical information infrastructure, respond to simulated cyber incidents under realistic pressure. Participation helps identify gaps in internal processes before a real incident exposes them, and it also strengthens coordination between individual businesses and national response mechanisms. Businesses that treat these exercises as a formality rather than a real test tend to gain far less value from participating.


One Comment